

Recently I went to log into my Shapeways account and, predictably, couldn't remember my password. Fine. I clicked "forgot login" and got the following:
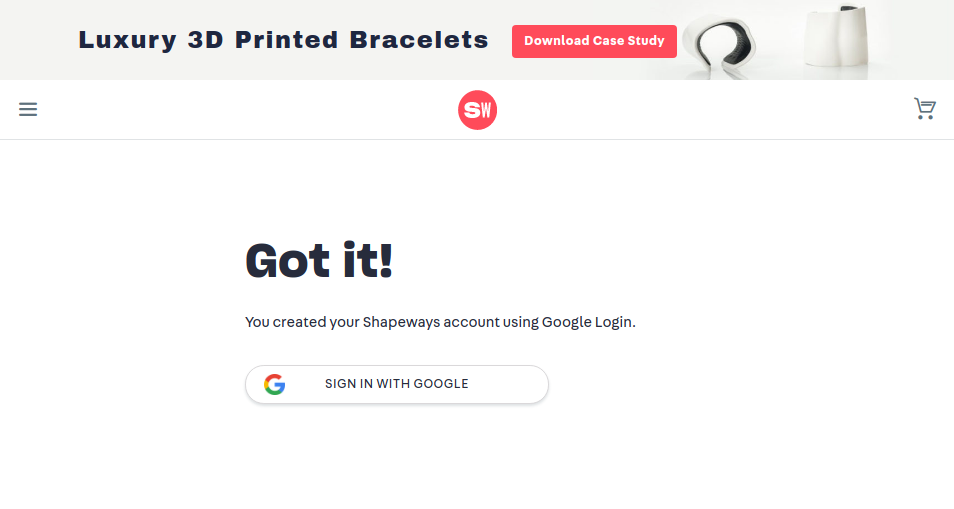
Not a password reset. Just a straight redirect to "Sign in with Google," because that's how I'd created the account in the first place. Harmless enough on its own, so I did what I always do on an auth page: I popped open DevTools before touching anything else.
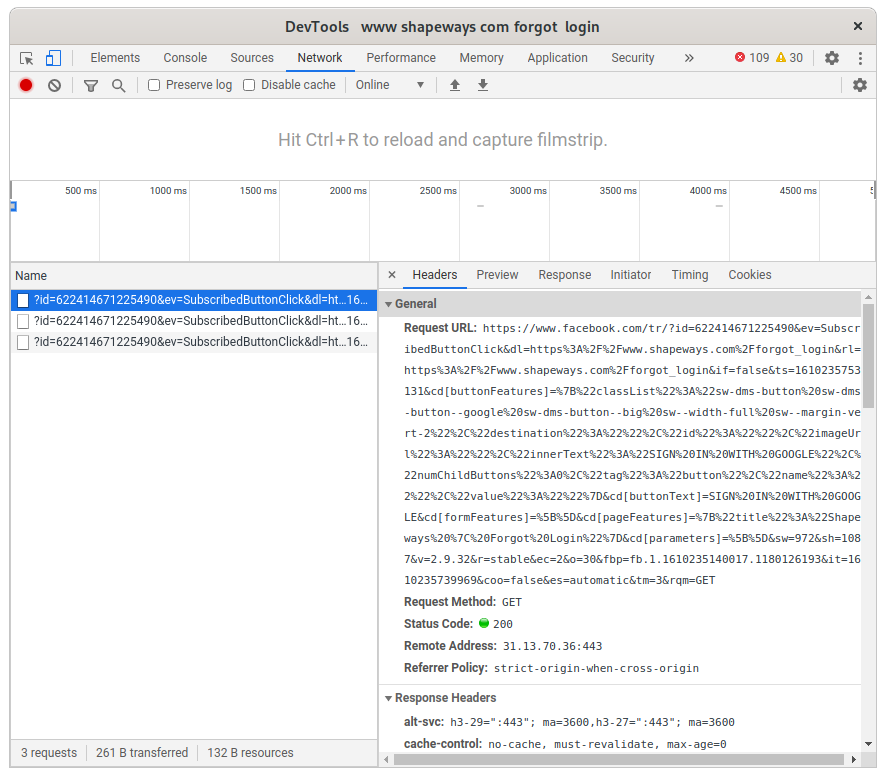
Sitting in the Network tab were three near-identical requests to
facebook.com/tr. That's the Meta Pixel, the little bit of JavaScript half
the web ships to feed Facebook's ad-targeting graph, and here it was firing on
a page whose entire purpose is "I am not currently authenticated and would
like to become authenticated again."
I flipped to the parsed view of the same request to read the payload cleanly:
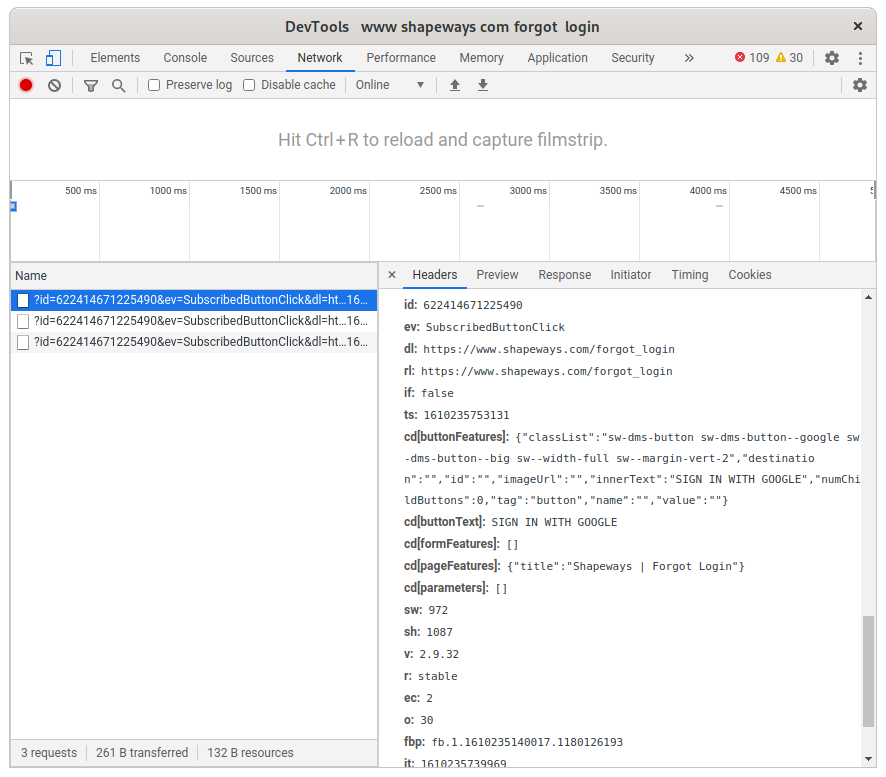
ev: SubscribedButtonClick. dl: https://www.shapeways.com/forgot_login.
cd[buttonText]: SIGN IN WITH GOOGLE. cd[buttonFeatures] carrying a
classList that includes sw-dms-button--google. cd[pageFeatures]
carrying the page title, Shapeways | Forgot Login. And, a few fields down,
an fbp value already attached, meaning Facebook has a durable identifier for
this browser regardless of whether I've ever logged into Facebook on it.
I grabbed the raw request URL and ran it back through a terminal, grepping for the word doing all the work, just to see it in isolation:
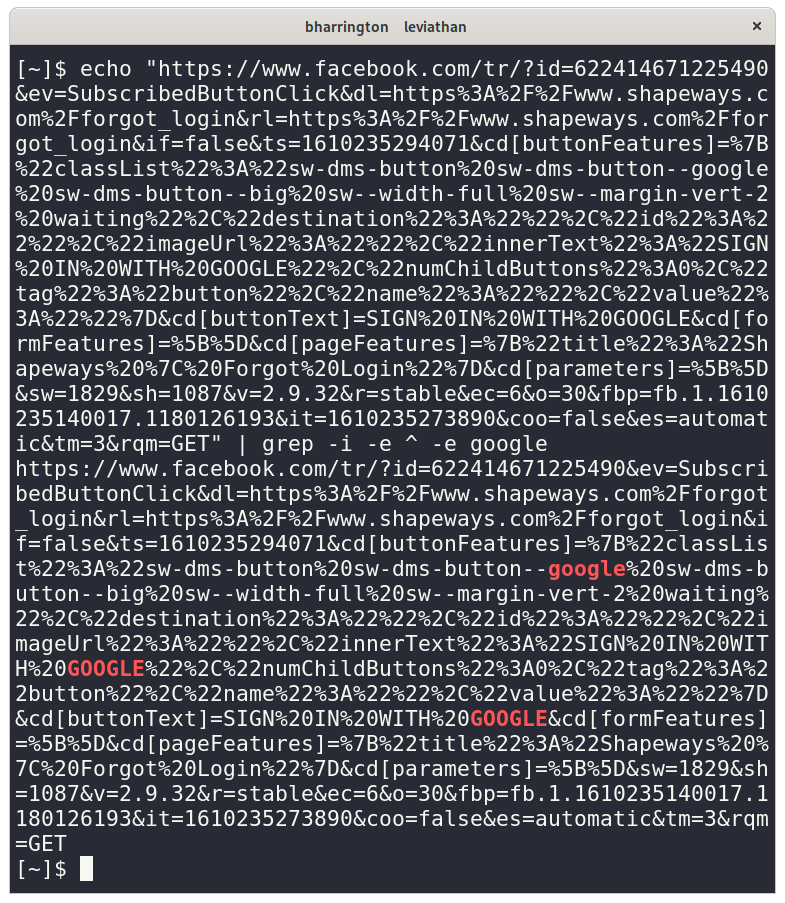
So here's what actually happened. A visitor who is, by definition, not logged in, on a page that exists specifically to help someone who has lost access to their own account, gets a request fired off to a third-party ad broker reporting that this specific browser is associated with a Shapeways account that authenticates through Google. Not a purchase. Not a page view. An identity-provider preference, tied to a persistent tracking cookie, shipped to Facebook by a button that sits on the one page where the visitor has proven the least about who they are.
I don't think anyone at Shapeways sat down and decided to leak authentication
metadata to an ad platform. I think someone wired up conversion tracking on
every button carrying sw-dms-button in its class list, the forgot-login page
happens to have one, and nobody ever asked whether that particular page
belonged on the list.
Goodjob Shapeways.